AI in development
AI Agents in Software Development: Speed Without Losing Quality
A practical guide to coding-agent tasks, human ownership, repository readiness, security, evaluations and a controlled adoption pilot.
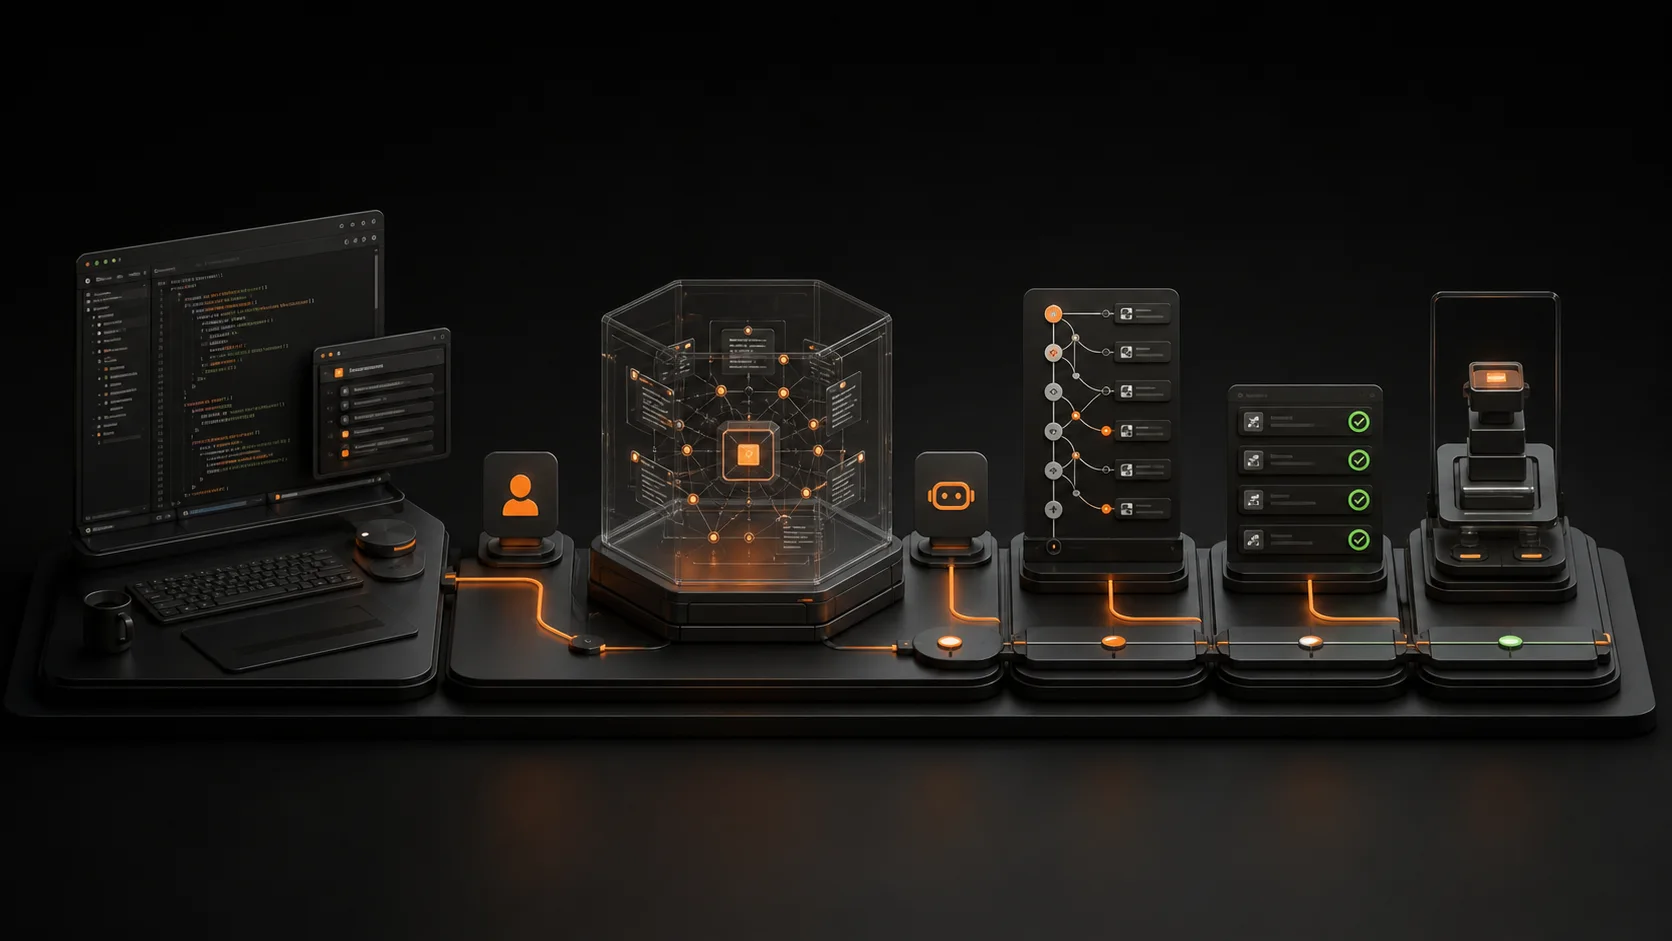
A software development agent is more than a chat interface or code completion tool. It receives a goal, studies a repository, calls tools, changes files and checks the outcome. It can take a connected task from analysis to a pull request, but the result still depends on context, constraints and engineering review.
The strongest gains rarely come from maximum autonomy. They come from a well-designed operating loop: a clear task, accessible documentation, a reproducible environment, automated tests, limited permissions and mandatory review for consequential changes.
How an AI agent differs from a coding assistant
A conventional assistant answers a request or suggests a code fragment. An agent works in a loop: it plans, reads files, calls tools, changes the codebase, observes the result and adjusts its next action. This lets it complete multi-step work instead of generating isolated functions.
Autonomy should not be uniform across every operation. Reading code and running local tests can be broadly allowed, while infrastructure changes, production data and release actions should require explicit approval.
- An assistant suggests; an agent executes a sequence of actions.
- Agents need tools, an execution environment and observable state.
- Permissions should follow the risk of each action.
- Architecture and release decisions remain with the team.
Software tasks that fit a coding agent
The best starting tasks have a clear outcome and a verifiable definition of done. Agents are useful when work spans several repository steps: identify affected modules, make a constrained change, update tests and prepare a concise explanation.
The higher the cost of an error, the narrower the operating boundary should be. Break work into units that can be verified through tests, static analysis, screenshots or before-and-after data checks before anything reaches production.
| Task | Agent contribution | Team control |
|---|---|---|
| Local bug fix | Finds the cause, changes code and adds a regression test | Diff review and CI |
| Small feature | Studies project patterns and implements an agreed flow | Requirements and UX review |
| Test coverage | Finds uncovered branches and adds tests | Scenario-quality review |
| Technical debt | Updates dependencies or repeated structures | Phased rollout and monitoring |
| Documentation | Reconciles code, run commands and API contracts | Module-owner review |
Where an agent cannot replace engineering judgment
An agent can pursue a stated goal, but it is not accountable for choosing the goal itself. It does not know hidden client agreements, acceptable operational risk or the reasons behind legacy architecture unless that context is made explicit.
Plausible changes that compile while breaking a business rule are particularly dangerous. Product requirements, data models, security, migrations and irreversible operations need a specialist who understands the wider system.
- Business goals and prioritization.
- Architecture and service boundaries.
- Financial, payment and legal rules.
- Data migrations and backward compatibility.
- UX acceptance and release decisions.
Preparing a repository for agentic work
Agents amplify order and expose its absence quickly. If the project cannot be installed reproducibly, tests are unstable and rules live only in one developer's memory, autonomous work will stop frequently or produce unpredictable results.
Useful context should be concise and current: run commands, module structure, constraints, naming rules, sources of truth and acceptance criteria. A large document archive without priority can be more distracting than helpful.
- One reproducible install and run path.
- Fast local checks plus a complete CI pipeline.
- Short instructions close to the code and clear module ownership.
- Isolated test data without production secrets.
- A task template with goal, boundaries and acceptance criteria.
Permissions, secrets and unintended actions
Agents may read external documents, issues and web pages, so untrusted content must never be treated as authority. Defence is layered: least privilege, sandboxing, secret filtering, approval for sensitive actions and a log of every tool call.
Access should be granted to a specific workflow rather than to the model in general. A documentation agent should not deploy, and a testing agent should not query customer records. This limits the impact of an error or prompt injection.
- Dedicated sandbox and temporary credentials.
- No secret or personal-data access without a real need.
- Approval before messages, payments or deployment.
- Action, diff, cost and source logs.
- A reliable stop mechanism and revocable access.
Why product tests are not enough
Unit and integration tests verify product behaviour, but they do not measure the quality of the agent workflow. Agents also need evals: representative tasks that measure whether the goal was achieved, constraints were respected and how many attempts were required.
Generated lines of code are a weak success metric. Track accepted changes, review time, rollbacks, post-release defects, execution cost and the frequency of human intervention instead.
- Share of tasks completed with verifiable evidence.
- Pull requests accepted without major rework.
- Time from task assignment to a ready change.
- Defects, rollbacks and security findings.
- Model and infrastructure cost per accepted task.
A controlled pilot for one team
Start with one repository and two or three task types. Record baseline time, quality and cost, then run the agent in a constrained environment and compare the outcome against the same criteria.
The pilot should decide more than which tool to buy. It should reveal which process needs improvement. Stronger tests, better task templates and concise documentation can create more value than simply changing the model.
- Choose repeatable, low-risk tasks.
- Prepare the environment, instructions and checks.
- Limit permissions and define mandatory approvals.
- Collect comparable before-and-after metrics.
- Expand only after stable results.
Frequently asked questions about coding agents
These are the questions teams usually ask before a coding-agent pilot. The exact architecture depends on the repository, infrastructure and data requirements.
A useful evaluation follows one real task from assignment to a verified result instead of comparing tools on abstract code generation.
Can an AI agent replace a software developer?
No. An agent can handle substantial execution work, but goals, architecture, risk ownership and final accountability remain with specialists.
Which tasks should a team start with?
Local bugs, tests, documentation and small features with clear acceptance criteria and automated verification are good starting points.
Should an agent have production access?
Permanent direct access is rarely necessary. A sandbox, least privilege and explicit approval for sensitive actions are safer.
How should ROI be measured?
Compare cycle time, accepted-change rate, review effort, defects, rollbacks and total execution cost before and after the pilot.
Does the project need a special architecture?
No special architecture is mandatory, but reproducible setup, tests, current instructions and clear module boundaries materially improve reliability.